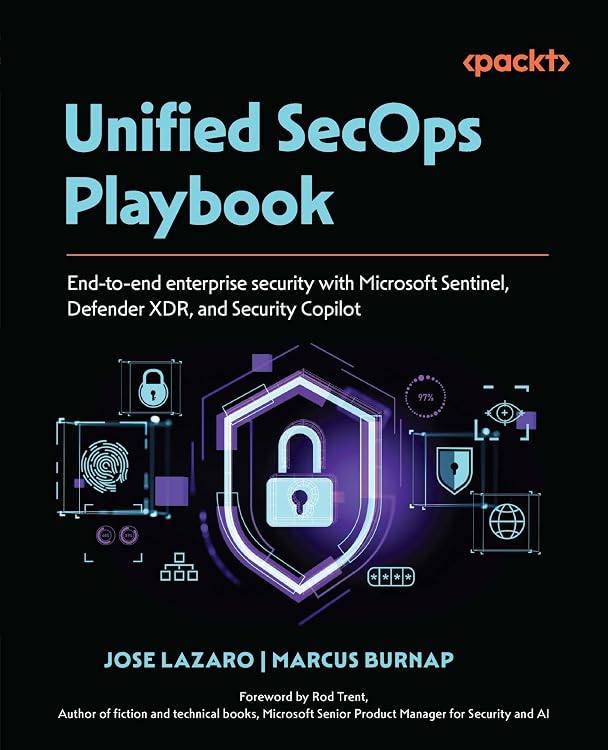
Unified SecOps Playbook: Microsoft Sentinel, Defender XDR and Security Copilot
Unified SecOps Playbook is a practical guide to Microsoft Sentinel, Defender XDR and Security Copilot for readers building or expanding Microsoft-focused security operations. It covers deployment, automation, Zero Trust, security frameworks and AI-assisted investigation, with an intended audience that already understands Microsoft security products and Azure.
At a glance
- Covers Sentinel deployment planning, secure architecture, RBAC, governance and financial planning.
- Includes KQL, detections, automation, MITRE ATT&CK and CI/CD deployment workflows.
- Discusses Security Copilot with Defender XDR for AI-assisted detection, investigation and response.
- Topics include Zero Trust, frameworks, DevSecOps, Entra ID, PIM and partner onboarding through Azure Lighthouse and GDAP.
- The listing says print or Kindle purchases include a free PDF eBook. Packt's Reader and PDF access require email sign-up and proof of purchase.
Reference price: $49.99
Price checked: Nov 14, 2026
View offerAhead of Black FridayExplore the selectionPros and cons
Pros
- Connects Microsoft Sentinel deployment with XDR, Security Copilot and operational workflows rather than focusing on a single tool.
- The listed topics include practical areas such as CI/CD, KQL, role-based access, cost planning and customer onboarding.
- The stated target audience includes security professionals moving from another SIEM to Sentinel.
Cons
- The book is aimed at readers who already have a solid understanding of Microsoft security products and Azure, so it may not suit beginners.
Technical specifications
7 specifications| Publisher | Packt Publishing |
|---|---|
| Publication date | December 31, 2025 |
| Language | English |
| Print length | 524 pages |
| ISBN-13 | 978-1837632862 |
| Weight listed | 1.96 pounds |
|---|---|
| Dimensions | 7.5 x 1.18 x 9.25 inches |
What to know before buying
- The complimentary PDF is described as included with print or Kindle purchases, while access to Packt's Reader and the PDF is subject to email sign-up and proof of purchase. Confirm the terms for the selected edition.
Who is it for?
A good fit for
- Security professionals with existing Microsoft security and Azure knowledge who want to expand into Sentinel.
- Teams planning Sentinel deployments, security automation, Zero Trust alignment or Security Copilot integration.
- Security experts considering Microsoft Sentinel alongside or in place of another SIEM.
Less suited to
- Readers seeking a beginner introduction to cybersecurity or Azure.
- Buyers looking for a general-purpose guide to non-Microsoft security platforms.
Customer reviews on Amazon
- 5 stars
100% 100% - 4 stars
0% 0% - 3 stars
0% 0% - 2 stars
0% 0% - 1 star
0% 0%
The supplied evidence contains only aggregate ratings, with a small sample shown entirely in the five-star category. That is an encouraging but limited signal and does not establish which parts of the book readers valued or how well its guidance works in practice. Buyers should judge fit mainly by its stated Microsoft-focused scope and its prerequisite knowledge of Azure and Microsoft security tools.
Frequently asked questions
Who is this book intended for?
The listing targets readers with a solid understanding of Microsoft security products and Azure, including security experts considering Sentinel as an additional or replacement SIEM.
What technical areas does the book cover?
Listed topics include Sentinel deployment and architecture, RBAC, governance, financial planning, KQL, detections, automation, CI/CD, Zero Trust, frameworks and Security Copilot.
Does the book include a PDF eBook?
The listing says print or Kindle purchases include a free PDF eBook. Email sign-up and proof of purchase are required for the described digital access.
Alternative options

The Ultimate Linux Shell Scripting Guide: Automate, Optimize, and Empower tasks with Linux Shell Scripting
$34.99
The Practical Network Engineer's Guide: Master routing, network diagnostics, and troubleshooting
$39.99
CompTIA® Network+® N10-009 Certification Guide: Master networking fundamentals and pass the N10-009 exam the first time
$30.39
Microsoft Security Operations Analyst Exam Ref SC-200 Guide: Achieve SC-200 Certification with Real-World Microsoft Security Operations Insights
$39.99
Agentic Architectural Patterns for Building Multi-Agent Systems: Proven design patterns and practices for GenAI, agents, RAG, LLMOps, and enterprise-scale AI systems
$41.99
Cyber Security Kill Chain - Tactics and Strategies: Breaking down the cyberattack process and responding to threats
$35.99
Microsoft Defender for Endpoint in Depth: Take any organization's endpoint security to the next level
$43.99
Agentic Coding with Claude Code: The everyday developer's guide to agentic coding with Claude Code
$32.78
Learn Microsoft Power BI: A comprehensive, beginner-friendly guide to real-world business intelligence
$44.99
CompTIA Security+ SY0-801 Study Guide: Exam-Focused V8 Reference with AI Threats, Exam Traps, and Every Answer Choice Explained, Plus an Online ... and Flashcards (IT Certification Exam Prep)
$39.99
Practical MCP Security: Defend agentic AI systems from supply chain, runtime, and code execution threats
$49.99
Mastering Ubuntu Server: Administer, secure, automate, and scale Ubuntu Server 26.04 for cloud, containers, and AI workloads
$39.99