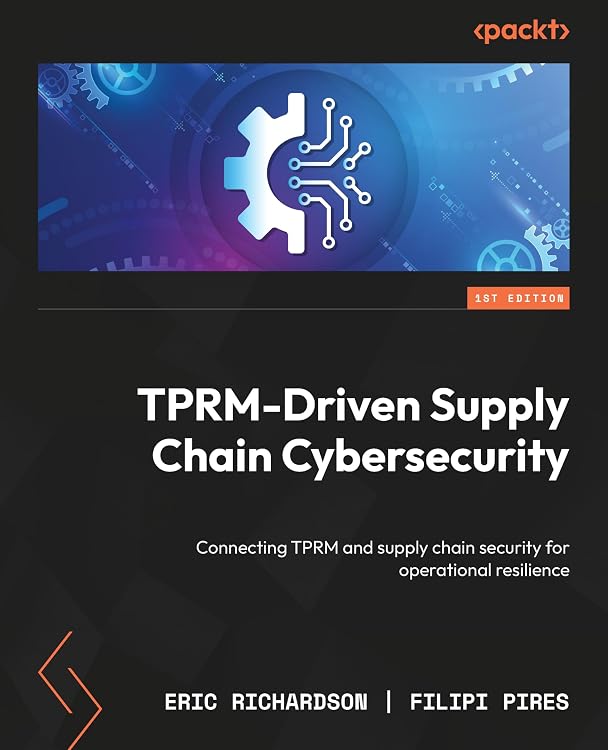
TPRM-Driven Supply Chain Cybersecurity
TPRM-Driven Supply Chain Cybersecurity is a Packt Publishing book about connecting third-party risk management with supply chain security. It outlines lifecycle-based vendor oversight, regulatory control mapping, contract practices, fourth-party risk, threat intelligence, and incident response, with adaptable assessment templates and playbooks listed among its resources.
At a glance
- Covers a vendor-risk lifecycle from onboarding through offboarding, including tiering and continuous monitoring.
- Discusses mapping DORA, GDPR, Executive Order 14028, NIST C-SCRM, and ISO/IEC 27036 guidance to controls and audit evidence.
- Includes topics on third- and fourth-party risk, security clauses, SBOMs, threat intelligence, and breach response.
- The listing says assessment templates, evidence checklists, and incident playbooks are included for adaptation.
Reference price: $44.99
Price checked: Nov 14, 2026
View offerAhead of Black FridayExplore the selectionPros and cons
Pros
- Connects procurement, legal, and security decisions rather than treating vendor assessments as isolated questionnaires.
- Addresses fourth-party exposure and critical subcontractors alongside direct supplier risk.
- Combines regulatory alignment with practical topics such as contract clauses, audit evidence, and incident playbooks.
Cons
- At 110 pages, the listed print edition is relatively concise for readers seeking extensive coverage of the many frameworks and program topics described.
Technical specifications
8 specifications| Publisher | Packt Publishing |
|---|---|
| Publication date | May 29, 2026 |
| Language | English |
| Print length | 110 pages |
| ISBN-10 | 1806708116 |
| ISBN-13 | 978-1806708116 |
| Weight listed | 1.3 pounds |
|---|---|
| Dimensions | 7.5 x 0.78 x 9.25 inches |
What to know before buying
- The description presents a broad set of frameworks and practices, but does not specify the depth or edition-specific coverage of each. Consider whether its stated basic familiarity with security and vendor management suits your background.
Who is it for?
A good fit for
- Cybersecurity leaders and TPRM or VRM practitioners building repeatable supplier oversight.
- Risk, procurement, compliance, and legal professionals working with vendor cybersecurity obligations.
- Readers seeking a practical introduction to fourth-party risk, SBOM diligence, and supplier incident planning.
Less suited to
- Readers seeking a general cybersecurity textbook or a detailed technical manual on implementing security tools.
- Readers with no familiarity with security principles or vendor management who need foundational instruction.
Customer reviews on Amazon
- 5 stars
0% 0% - 4 stars
0% 0% - 3 stars
0% 0% - 2 stars
0% 0% - 1 star
100% 100%
The supplied aggregate rating is very low, but it represents only one rating and no written feedback is provided. That is too limited to identify specific strengths, problems, or how well the book's stated coverage works in practice. Buyers should assess the listed topics and intended audience directly.
Frequently asked questions
What does this book cover?
The listing describes vendor risk management across onboarding to offboarding, regulatory and control mapping, contract terms, fourth-party exposure, threat intelligence, SBOMs, and incident response.
Which frameworks and regulations are mentioned?
The description names DORA, GDPR, Executive Order 14028, NIST C-SCRM, and ISO/IEC 27036. It also says compliance teams working with HIPAA and related requirements may benefit.
Does it include practical resources?
The listing says it includes adaptable assessment templates, evidence checklists, and incident playbooks. It does not specify their quantity or format.
Who is the intended reader?
The stated audience includes cybersecurity leaders, TPRM and VRM practitioners, risk managers, procurement professionals, compliance teams, and in-house counsel. Basic familiarity with security and vendor management is suggested.
Alternative options
Advanced Cyber Threat Intelligence and Hunting: Detect APTs and zero-day attacks using CTI, behavioral analytics, and AI techniques
$49.99
Agentic Architectural Patterns for Building Multi-Agent Systems: Proven design patterns and practices for GenAI, agents, RAG, LLMOps, and enterprise-scale AI systems
$41.99

The Ultimate Linux Shell Scripting Guide: Automate, Optimize, and Empower tasks with Linux Shell Scripting
$34.99
Agentic Coding with Claude Code: The everyday developer's guide to agentic coding with Claude Code
$32.78
The Practical Network Engineer's Guide: Master routing, network diagnostics, and troubleshooting
$39.99
Mastering Ubuntu Server: Administer, secure, automate, and scale Ubuntu Server 26.04 for cloud, containers, and AI workloads
$39.99
Practical MCP Security: Defend agentic AI systems from supply chain, runtime, and code execution threats
$49.99
Yocto Cookbook: Practical recipes for building and maintaining production-ready embedded Linux systems
$29.99