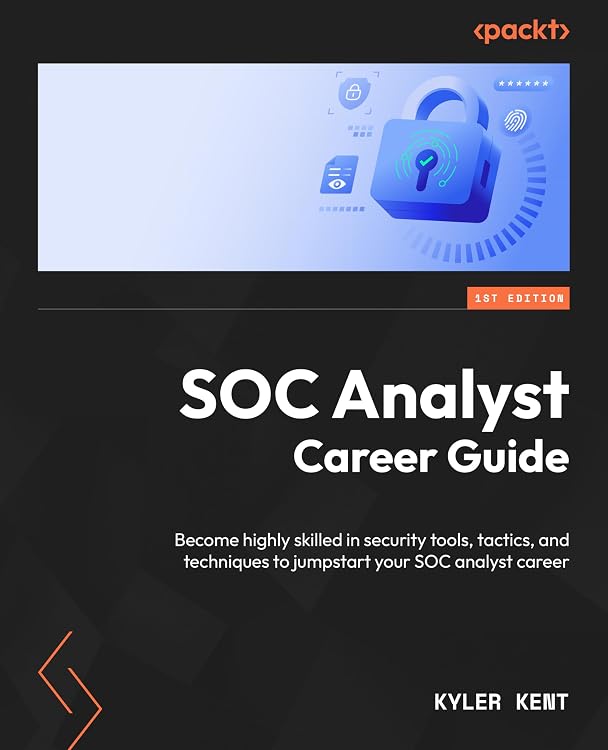
SOC Analyst Career Guide: SIEM, Security Operations and Career Preparation
SOC Analyst Career Guide is a 600-page English book covering security operations, analyst workflows, SIEM, threat investigation and career preparation. Its described material ranges from core SOC roles to detection engineering, incident response, security tools, home-lab planning, portfolios and interviews.
At a glance
- Covers SOC fundamentals, analyst duties, SIEM, triage and investigation, with hands-on labs and scenario-based exercises described in the listing.
- Topics include detection engineering, incident response, forensics, recovery, endpoint, network and web application security.
- Career-focused material includes portfolio development, job searching and interview preparation.
- The listing describes home-lab development using an operational SIEM and EDR solution.
Reference price: $44.99
Price checked: Nov 14, 2026
View offerAhead of Black FridayExplore the selectionOften bought together
Pros and cons
Pros
- Connects technical SOC topics with practical career preparation, including portfolios and interview skills.
- Broad subject coverage spans blue-team and red-team tools, incident response, forensics, network security and web application security.
- Hands-on labs and scenario practice are part of the described approach.
Technical specifications
8 specifications| Publisher | Packt Publishing |
|---|---|
| Publication date | December 23, 2025 |
| Language | English |
| Print length | 600 pages |
| ISBN-10 | 1835467466 |
| ISBN-13 | 978-1835467466 |
| Listed weight | 2.24 pounds |
|---|---|
| Dimensions | 7.5 x 1.36 x 9.25 inches |
What to know before buying
- The listing says PDF access and Packt Reader access are free with the book, but requires email sign-up and proof of purchase. A separate description also mentions an AI assistant, so confirm which digital extras are currently available.
Who is it for?
A good fit for
- People preparing for entry-level SOC analyst work or considering a role at a security operations center or managed security services provider.
- Readers seeking an overview that combines SOC operations and security tools with job-search and interview guidance.
- Learners who already have basic networking and computer skills, as recommended by the listing.
Less suited to
- Readers seeking a specialist reference focused only on one SIEM platform, certification exam or security discipline.
- Complete beginners without basic computer and networking knowledge, since the listing says these foundations are needed to follow the material with ease.
Customer reviews on Amazon
- 5 stars
100% 100% - 4 stars
0% 0% - 3 stars
0% 0% - 2 stars
0% 0% - 1 star
0% 0%
The listing shows a five-star aggregate based on a very small rating sample. That is too little evidence to establish broad customer sentiment or identify specific strengths or problems.
Frequently asked questions
What topics does the book cover?
The listing describes SOC roles and operations, SIEM, triage, threat investigation, detection engineering, incident response, forensics, endpoint and network security, and web application security.
Does it include practical exercises?
The listing says it includes hands-on labs, exercises and scenario-based training, and describes developing a home lab with an operational SIEM and EDR solution.
Is it aimed at beginners?
It is aimed at people interested in becoming SOC analysts, but the listing recommends basic networking and computer skills to follow the material more easily.
Are digital copies or tools included?
The listing claims free PDF and Packt Reader access with the book and says email sign-up and proof of purchase are required. It also mentions an AI assistant elsewhere, so confirm availability and exact included digital features.
Alternative options
PowerShell Automation and Scripting for Cybersecurity: Hacking and defense for red and blue teamers
$32.60
Cybersecurity Terminology & Abbreviations- CompTIA Security Certification: a QuickStudy Laminated Reference Guide
$7.41
Effective Threat Investigation for SOC Analysts: The ultimate guide to examining various threats and attacker techniques using security logs
$41.99
Digital Forensics Cookbook: Field-Tested Recipes for Real-World Investigations Across Windows, macOS, Linux, iOS, and Android
$35.99
Blue Team Handbook: SOC, SIEM, and Threat Hunting (V1.02): A Condensed Guide for the Security Operations Team and Threat Hunter
$43.65
CompTIA® Network+® N10-009 Certification Guide: Master networking fundamentals and pass the N10-009 exam the first time
$30.39
Multi-Agent AI Engineering: Design, build, and operate AI systems that think and act as coordinated teams
$52.24
AI Evals in Practice: Testing, reliability, and quality for LLM systems in production
$34.99

Advanced Cyber Threat Intelligence and Hunting: Detect APTs and zero-day attacks using CTI, behavioral analytics, and AI techniques
$49.99
Building the Agentic Enterprise: A Practical Field Guide to Designing, Deploying, and Operating Agentic AI Systems on Google Cloud
$43.99
The Practical Network Engineer's Guide: Master routing, network diagnostics, and troubleshooting
$39.99
Enterprise AI Agent Security: A Practical Guide to MCP Security, Prompt Injection Defense, RAG Security, and Agentic AI Governance
$47.99